Ease of Use
+7 pts above avg
95%
IA
95%
AVG
88%

Recherches, guides et analyses concrètes sur la surveillance d'examens en ligne ; pour aider votre programme à obtenir des résultats équitables, fiables et défendables.
Évaluations sécurisées
Violations de données en plus de 12 ans
Taux de fidélisation client
Ressources publiées
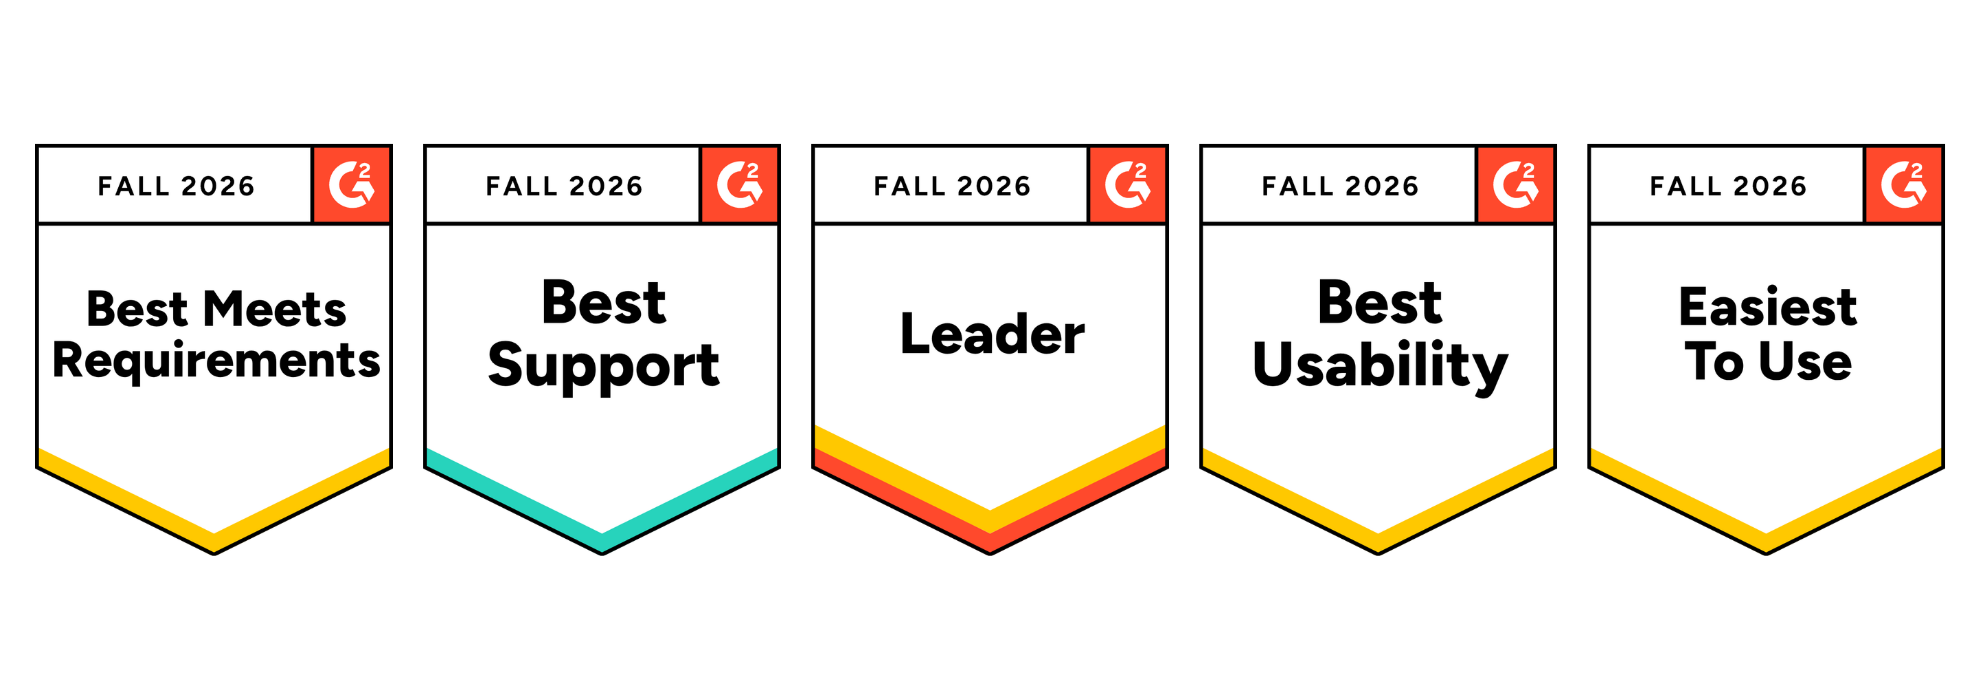
Integrity Advocate has been ranked #1 for Online Proctoring Usability on G2 for the third consecutive season. Based on verified customer feedback, we also earned five Fall 2026 badges recognizing usability, ease of use, support, and overall leadership.
Integrity Advocate has once again been ranked #1 in G2’s Usability Index for Online Proctoring, marking our third consecutive season at the top of the category.
In the Fall 2026 report, Integrity Advocate earned an overall G2 Index Score of 8.60, ahead of Honorlock, Proctorio, Quilgo, Talview, and Meazure Learning. We also earned five G2 badges, including Best Usability, Easiest to Use, and Best Meets Requirements, and were recognized as a Leader in the online proctoring category.
These recognitions are based on feedback from verified users. For us, that is what makes them meaningful. They reflect the experiences of the people who administer assessments, support test takers, and rely on the results.
Integrity Advocate earned the highest overall score in the Fall 2026 Online Proctoring Usability Index:
This is not only another first-place ranking. Our overall index score increased from 8.45 in Summer 2026 to 8.60 in Fall 2026, extending Integrity Advocate’s position at the top of the category.
G2 is the largest peer-to-peer software review platform in the world. Their Usability Index ranks products within a category based on three user-rated dimensions:
Every score comes from authenticated, verified reviews. Companies cannot pay to improve their position. There is no sponsorship or placement influencing the results. The index score reflects what users say about their experience with the product.
Integrity Advocate scored above the online proctoring category average across every usability measure included in the report:
User adoption stands out in particular. Integrity Advocate scored 17 points above the category average and 28 points above Honorlock.
That matters because a platform can have an impressive feature list and still create friction when people are asked to use it. Strong adoption suggests that the experience works in practice, not only during a product demonstration.
In addition to ranking first in the Usability Index, Integrity Advocate earned five G2 badges for Fall 2026 and was recognized as a Leader in online proctoring.
The Best Usability, Easiest to Use, and Best Meets Requirements badges reinforce something we have always believed: assessment security should be strong without being unnecessarily complicated.
Organizations should not have to choose between protecting an assessment and delivering an experience people can successfully use.
Online proctoring sits at a sensitive point in the assessment experience. Test takers may already be under pressure, while administrators need to protect exam integrity without creating unnecessary technical problems or support demands.
A platform that is difficult to access or manage can lead to:
Integrity Advocate was designed to remove those barriers.
There is no software to install and no browser extension to manage. The platform works across devices and browsers and integrates into existing assessment workflows. Test takers can access their assessments without navigating a separate, unfamiliar system, while administrators gain clear evidence and the context needed to evaluate results.
Usability is not separate from assessment integrity. When a platform works consistently, more attention can remain where it belongs: on the assessment and the credibility of its outcome.
Ease of use should never require an organization to compromise on accuracy or defensibility.
Integrity Advocate combines intelligent detection with Verified Human Review™ to provide context behind potential assessment violations. Instead of asking administrators to make decisions based only on an automated flag, our proctoring solutions can provide a clear, reviewable record supported by human judgment.
The result is an approach that protects assessment integrity while remaining practical for the people responsible for administering the program and fair to the people taking the assessment.
Across reviews, users consistently highlight the qualities reflected in the Fall 2026 report: straightforward implementation, ease of use for learners and administrators, seamless LMS integration, responsive support, and a privacy-first approach to assessment integrity.
As one verified user shared:
{{post-block-quote}}
That experience is what the rankings ultimately represent. Not simply a score, but whether the platform helps organizations protect assessments without placing unnecessary friction on their teams or test takers. View more customer stories here.
If you are currently comparing online proctoring solutions, usability should be evaluated alongside security, privacy, and review quality.
Consider asking:
The Fall 2026 G2 results provide an independent view of how leading platforms perform across many of these considerations.
Being ranked #1 once is exciting. Remaining at the top for three consecutive seasons tells a stronger story.
It shows that organizations do not have to accept unnecessary complexity as the price of protecting their assessments. Online proctoring can be secure, privacy-first, easy to administer, and straightforward for test takers.
That is the experience Integrity Advocate was built to provide, and we are grateful to every customer who shared their experience on G2.
The G2 ranking reflects a platform that has been in continuous operation for over a decade:
{{post-cta}}
September 25, 2026
|
5 min de lecture
A little preparation before exam day goes a long way. Our Customer Success team shares four simple steps that help learners feel ready and cut down on avoidable support issues and flags.
One of the easiest ways to make online proctoring feel smoother is also one of the simplest: make sure learners know what to expect before assessment day. A lot of the friction we see isn’t really about the assessment itself. It comes from uncertainty. Learners are trying to figure out what technology they need, whether everything will work properly, what they’re allowed to have with them, and where to go if something doesn’t behave the way they expect. A little preparation ahead of time can make a big difference.
Before learners begin, they should know what the proctoring experience will look like and what will be expected of them. Every learner will need a webcam and photo ID. Depending on the assessment setup, they may also need a microphone or to meet specific testing-environment requirements. Sharing the appropriate Integrity Advocate What to Expect resources ahead of time gives learners a chance to understand the process before they’re already sitting down to take an exam.
Useful learner resources include:
Finding out five minutes before an exam that something isn’t working is stressful for everyone.
Every Integrity Advocate What to Expect page includes a trial that learners can test ahead of time. The trial includes a system check, so they can confirm that their device, browser, webcam, microphone where required, and internet connection are ready before they sit down for the real assessment.
Encouraging learners to complete the trial ahead of time also gives them a chance to get familiar with the process and resolve any technical issues when there isn’t an exam clock running.
If they do run into an issue, the Integrity Advocate Support Center includes troubleshooting resources for common technical problems: Support Center
This is one of the biggest things I recommend to clients. If notes are allowed, say so. If phones aren’t allowed, say so. If learners can use a calculator, secondary device, blank paper, or specific reference material, make that clear before they begin.
Just as importantly, make sure anything that is allowed is also added to the Allow List in your rule settings. Telling learners they can use something isn’t enough if the platform is still configured to flag it.
Integrity Advocate can monitor and document what happens during a session, but the rules in the platform need to match the rules you’ve communicated to learners.
Clear instructions and aligned rule settings reduce confusion for the learner, cut down on avoidable flags, and make the review process much easier to interpret afterward.
Learners shouldn’t have to hunt around for help in the middle of an assessment.
Sharing the Integrity Advocate Support Center ahead of time gives them a clear place to go if they run into technical issues during setup, testing, or the assessment itself: https://www.integrityadvocate.com/support-center
It’s also helpful to be clear about which questions should come back to the school, training provider, or certification organization. Things like:
generally still need to be handled by the organization administering the assessment.
The technology is only one part of a successful proctoring experience. When learners know what to expect, have tested their setup, understand the rules, and know where to get help, assessment day becomes much less intimidating.
From the Customer Success side, that preparation usually means fewer avoidable support issues, fewer unnecessary flags, and a smoother experience for learners and administrators alike.
A little communication before exam day does a lot of heavy lifting.
September 24, 2026
|
5 min de lecture
Scaling assessment volume usually means scaling IT overhead right alongside it. Here's how programs like BCIT and NPI run thousands of concurrent exams without adding support burden.
Most assessment programs hit the same wall on the way to scale. Exam volume grows, and IT workload grows right along with it: more devices to support, more compatibility issues, more help desk tickets on exam day. Volume and overhead move together, so scaling the program means scaling the support burden too.
It doesn't have to work that way. The programs that scale cleanly aren't the ones with bigger IT teams. They're the ones that removed the dependency on IT in the first place.
The strain usually traces back to one decision made early: whether the proctoring tool runs in the browser or requires something installed on the device.
An install-based tool means every concurrent exam is also a concurrent support surface. Different operating systems, different browser versions, corporate devices with restricted permissions, personal laptops that can't install anything new. Multiply that by a few thousand simultaneous sessions and the IT team isn't supporting an exam anymore. They're running an incident desk.
None of that has anything to do with assessment security. It's friction created by the delivery method, and it scales in the wrong direction: the more successful the program gets, the worse the problem becomes.
Browser-based delivery removes the install dependency entirely. Test takers launch directly from the LMS, on any device, on any browser, with no extension or client software to manage. Identity verification happens automatically at check-in rather than through a separate application. There's nothing for IT to pre-approve, image onto lab computers, or troubleshoot when a candidate's device won't cooperate an hour before their exam window opens.
At low volume, this difference is a convenience. At high volume, it's the entire reason a program can grow without growing its support headcount to match.
The cost of IT overhead rarely shows up as a line item. It shows up as delayed rollouts, exam-day escalations, and staff time pulled away from the program itself to handle device issues that have nothing to do with academic or credentialing integrity. At scale, that cost compounds. A support model that handles a few hundred sessions without strain can buckle at a few thousand, and the failure point usually appears on exactly the day it can least afford to: exam day, with the least room to absorb disruption.
BCIT moved 13,000 remote exams through a single semester, mid-year, with a full transition to D2L Brightspace built in. Only about 1% of students needed support at all. That's not a small deployment absorbing a spike. It's a program running at real institutional volume without the support burden scaling alongside it.
The National Payroll Institute proctored more than 30,000 exams with a sub-1% support rate, alongside a 57% reduction in academic integrity incidents. The two results aren't separate wins. They're the same design decision showing up twice: remove the friction that creates support tickets, and the program can scale without adding the overhead that usually comes with it.
Removing IT overhead solves the delivery problem, but delivery is only half of what scale tests. The other half is whether every flagged session still gets a documented, human-reviewed outcome when volume climbs into the thousands.
This is where platforms that rely purely on automated detection start to show strain in a different way. Automated flags scale easily. Defensible decisions don't, unless the review process was built to scale with them. A trained reviewer examining every flagged session, not just the automated ones, is what keeps a result defensible at exam five and at exam five thousand.
A few questions separate a platform that scales cleanly from one that quietly shifts the burden onto your team:
If the answer to any of these points back toward more internal overhead as volume grows, that's the overhead that will show up later, usually during the busiest exam window of the year.
Running thousands of concurrent exams shouldn't require thousands of IT hours to support them. A program built to scale cleanly separates volume from overhead from the start, so growth means more exams delivered, not more support tickets filed. That's what makes results fair, trustworthy, and defensible at any scale the program reaches.
{{post-cta}}
March 25, 2026
|
5 min de lecture
AI has made assessment integrity impossible to ignore. For associations running certification and continuing education programs, the stakes are high - your credentials are only as valuable as the trust behind them. In this 30-minute session, TopClass and Integrity Advocate break down what the rise of AI means for online assessments and what associations can do about it today.
Click Here to Access the On-Demand Webinar
This webinar explained how generative AI has changed certification risk. Brandon Smith showed how candidates can now move through course content quickly, use AI tools to answer questions, or mask identity through virtual cameras and cloned video feeds. The session focused on a practical response: Privacy-First monitoring, identity verification, metadata checks, and Human-Reviewed decisions that give programs evidence they can defend.
Edward Wendling then showed how the TopClass integration works in practice. Administrators choose which assessments need proctoring, turn Integrity Advocate on for those activities, and publish everything inside the learning experience they already manage in TopClass. Learners stay in one workflow, complete a guided setup, and take the assessment in TopClass while monitoring runs in the background. After the session, reviewers evaluate flagged events so organizations can hold results for review when needed and release trusted outcomes with a stronger record behind every credential.
The webinar covered AI-assisted cheating, autonomous test-taking tools, virtual cameras, and cloned identities. The point was clear: certification programs now need evidence that reaches beyond a score report.
TopClass clients can choose which exams need proctoring, configure the rules for each assessment, and keep learners in the same course and testing flow they already know. That keeps rollout simpler for administrators and candidates.
The speakers showed why the LMS, the proctoring layer, and the credentialing system need to work together. When those systems share verified outcomes, you can issue credentials with stronger confidence and clearer audit trails.
{{post-cta}}
September 17, 2026
|
5 min de lecture
Your organization, not your proctoring vendor, carries the liability under GDPR and PIPEDA. This guide breaks down exactly what each law requires and the five questions to ask before you sign.
When a testing result gets challenged, and eventually one will, the first question isn't whether your proctoring vendor was compliant. It's whether you can prove it.
Under both GDPR and PIPEDA, liability for how personal data is collected, stored, and used sits with the organization running the assessment, not the vendor supplying the software. Regulators and courts have been consistent on this point: the vendor is the data processor, but the organization deploying that vendor is the data controller, and controllers carry the accountability. That distinction matters far more than most procurement checklists reflect.
This means your proctoring vendor isn't just a feature set. It's part of your compliance posture. Before you sign, you need to know exactly what they can document, not just what they claim.
GDPR applies to any organization handling data belonging to EU residents, regardless of where that organization is based. For online assessment specifically, seven principles apply directly:
GDPR adds two further requirements on top of those seven principles, and both are worth checking closely. The first is "privacy by design," a separate obligation under Article 25 requiring that data protection be built into the product from the start, not layered on afterward as a policy update. The second is consent: it has to be freely given, specific, informed, and unambiguous. A checkbox buried in terms of service doesn't meet that bar.
PIPEDA remains Canada's governing federal privacy law for private-sector organizations. Its 10 Fair Information Principles, set out in Schedule 1, cover accountability, identifying purposes, consent, limiting collection, limiting use and disclosure, retention, accuracy, safeguards, openness, and individual access. For proctoring specifically, three principles carry the most weight:
Limiting collection. The vendor should only be capturing what's needed to verify identity and confirm participation, nothing else.
Retention and disposal. Personal information shouldn't be held longer than necessary to fulfill its original purpose. If your vendor can't tell you exactly when biometric or ID data is deleted, that's a gap.
Safeguards. Protection has to be proportionate to the sensitivity of the data. Government ID and biometric data are among the most sensitive categories a vendor will ever touch.
Most vendor evaluations stop at "are you GDPR compliant?" That's not specific enough to protect your organization. Ask these instead:
If a vendor can't answer these clearly and specifically, you're the one holding the risk when a regulator or a challenged candidate comes asking.
A proctoring vendor built for this standard should be able to show you specifics, not principles. That looks like: identity capture limited to what's actually needed (not full document scans retained indefinitely), biometric processing that happens on the user's device rather than being transmitted and stored, sensitive images and ID data deleted on a fixed schedule measured in hours, not months, and data residency options that let you keep information within a specified jurisdiction by default.
It also means the compliance story doesn't end at data handling. When a session gets flagged, the record needs to include not just the automated signal but a trained reviewer's documented judgment. That's the difference between a flag and a decision, and it's the difference between a result you can defend and one you can't.
Every proctoring vendor will tell you they take privacy seriously. Few can produce the documentation to back it up on demand: the retention schedule, the data flow diagram, the access log, the reviewer's reasoning behind a specific outcome. That documentation is what actually protects your organization and your reputation when a regulator, an auditor, or a challenged candidate asks you to show your work.
Integrity Advocate is built around exactly that standard: privacy-first data handling paired with human review on every flagged session, so every outcome your program issues is fair, trustworthy, and defensible.
{{post-cta}}
September 9, 2026
|
5 min de lecture
CXC's 2026 results show exam irregularities nearly doubling since 2023, with AI misuse tracked as a distinct violation category for the first time. The takeaway for certifying bodies: automated detection is built to flag behavior, not to judge intent, and AI-assisted cheating often leaves no behavioral signal at all. Human review is what turns an automated flag into a decision a program can defend when a result is challenged.
The Caribbean Examinations Council logged 128 exam irregularity cases in its 2026 CSEC and CAPE sittings, up from 80 the year before, 54 in 2024, and 36 in 2023. For the first time, CXC tracked AI misuse as its own distinct violation category, alongside unauthorized devices, collusion, and prohibited materials.
Dr. Nicole Manning, CXC's Director of Operations, called it plainly: "The new one on the block, AI misuse. We have never had this before. This is new."
That last part is worth sitting with. CXC is not a small regional testing operation experimenting with online delivery for the first time. It's one of the most established certifying bodies in the Caribbean, running high-stakes exams that determine university admission and professional standing for hundreds of thousands of candidates every year. If an organization with that much institutional experience is only now building a category for AI misuse, it means the problem outpaced the systems built to catch it. CXC has already published standards and guidelines for responsible AI use in assessments, which suggests this isn't a body caught flat-footed. It's a body that's still catching up to how fast the problem is moving.
Traditional automated proctoring is built to flag behavior: eye movement, tab switching, background noise, a second voice in the room. Those signals work reasonably well for older forms of misconduct, like a hidden phone or a collaborator in the next room.
AI-assisted cheating doesn't produce those signals. A candidate quietly generating or paraphrasing an answer with an AI tool doesn't look different on camera from a candidate thinking hard about a question. There's no unusual eye movement to flag, no device to detect, no second voice to hear. The behavior that automated systems are built to catch simply isn't present, a gap we've written about in more detail in why hybrid AI plus human review delivers fairer, more accurate proctoring.
This is precisely the gap CXC's numbers point to. Unauthorized devices and collusion are the kinds of violations automated flags are designed for, and they're still the largest categories. AI misuse is different. It's a violation type that had to be created because the existing detection model didn't have a place for it, and likely wasn't catching all of it either.
Here's the distinction that matters for any certifying body watching this trend: an automated system can tell you that something looked unusual. It cannot tell you whether that pattern constitutes a violation. That determination needs context, judgment, and a person willing to make a defensible call, which is the core question we walk through in AI-only, live, or hybrid: which proctoring model is right for your program.
This is where the stakes get real for certifying bodies specifically. When CXC cancels a grade or disqualifies a candidate for an irregularity, that decision affects university admission, professional licensure, or the credibility of the credential itself. If that decision was made on an automated flag alone, with no human confirming that the flag actually represents misconduct, the certifying body is exposed. A candidate who disputes the finding, and many will, needs to see more than "the algorithm flagged it." They need a documented, reasoned judgment behind the decision.
That's not a hypothetical risk. It's the exact scenario CXC is now managing at scale, with a new violation category and no established playbook for how to review it consistently.
CXC operates one exam program in one region, but the underlying shift applies everywhere. As AI tools become more capable and more available, every certifying body issuing high-stakes credentials is facing the same exposure: automated-only proctoring was built for a threat model that no longer covers the most common form of cheating. We go deeper on what this shift means for programs specifically in AI cheating and assessment integrity in 2026.
This doesn't mean certifying bodies need to abandon automation. It means automation alone is no longer sufficient to defend the results a program issues. A trained reviewer examining every flagged session, not just the ones an algorithm surfaces, is what turns a flag into a decision that can withstand a challenge.
For programs issuing credentials that carry real weight, whether that's a school leaving certificate, a professional designation, or a regulatory license, the question worth asking isn't whether AI misuse will show up in the exam room. CXC's numbers suggest it already has. The question is whether the program has a defensible way to handle it when it does.
{{post-cta}}
August 21, 2026
|
5 min de lecture
At ASAE Annual, it was clear that continuing education has become a strategic driver of member value, revenue, and reputation. As associations scale learning online, verification and assessment integrity are essential to ensuring every credential remains credible and meaningful.
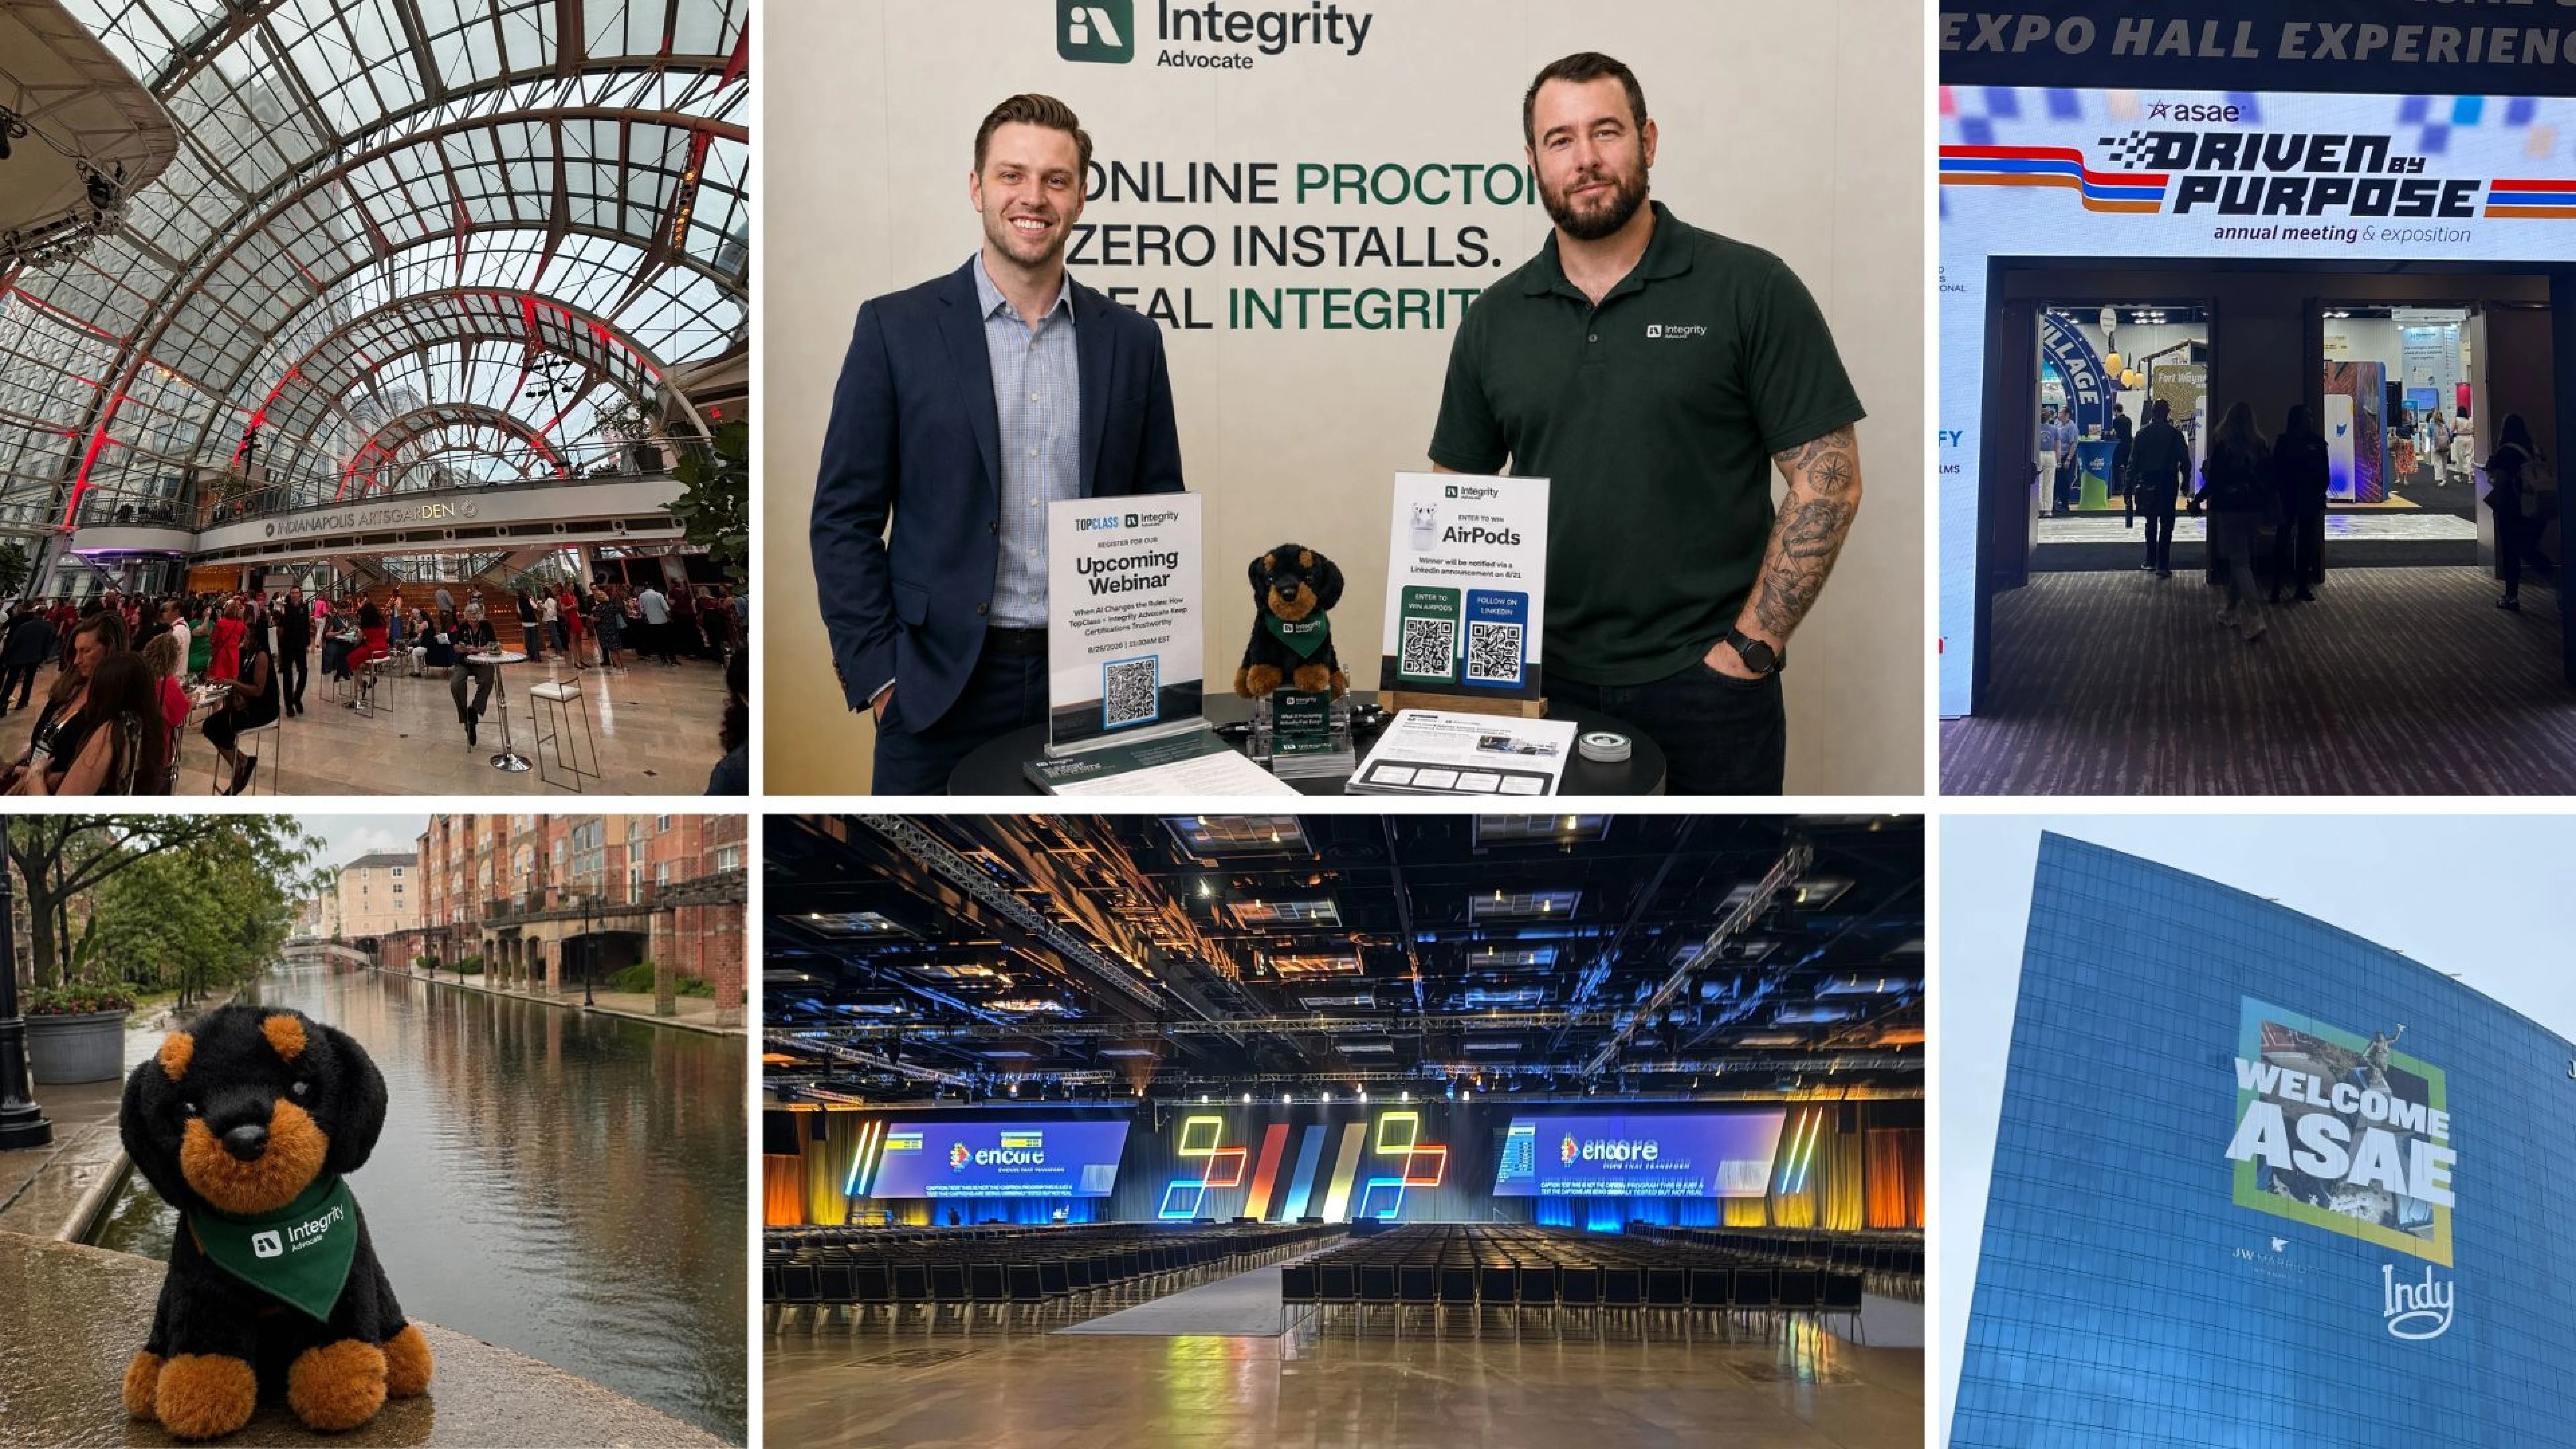
I just got back from ASAE's Annual Meeting in Indianapolis, and I'm still working through everything I heard. If you've never been, ASAE Annual is the biggest gathering of association executives in the country, and this year's theme was Driven by Purpose. That framing turned out to fit the week better than I expected, because the show floor and the session rooms were both buzzing with the same underlying question: what does it actually mean to serve your members well right now?
I went in expecting to hear a lot about membership growth and event strategy. I came home with something different. Almost every conversation I had, whether it was in a session, at a sponsor booth, or over coffee between keynotes, eventually circled back to learning. Specifically, how associations build it, how they prove it works, and how they protect it once it's out in the world.
For a long time, a lot of associations treated their learning and CE offerings as a member benefit that lived somewhat separately from the core business. Nice to have, good for retention, not exactly mission-critical. That framing is gone.
What I heard over and over in Indianapolis is that association leaders now think about learning the way they think about credentialing: as a structured, accountable framework, not a loose collection of webinars and one-off workshops. IACET came up constantly, and for good reason. Getting IACET accredited and issuing verifiable CEUs isn't a box to check anymore, it's how associations signal that their education actually meets a recognized standard. That shift, from informal to formal, from "nice to have" to genuinely important, is probably the single biggest theme I took away from the whole week.
Related to that first point: I sat in on more than one session where association leaders talked about the actual return on investing in properly structured continuing education. It's not just about compliance or member satisfaction scores. Strong CE programs are becoming a genuine revenue line and a genuine reputational asset. Members are willing to pay for training they trust. Employers are willing to sponsor it. Regulators and licensing bodies are willing to recognize it. But none of that works if the learning underneath it is soft. The associations getting this right are the ones investing in real instructional design, real assessment, and real verification, not just slapping a certificate on the end of a video.
This was the idea that really took some time to realize, and it came from a presentation from Bill Sheehan, Global Head of Association Strategy at D2L. Bill put it something like this: associations are no longer striving just to be relevant, they need to strive to provide impact.
At first that sounds like a subtle rewording. It isn't. Relevance is a passive approach. It's about staying in the conversation. Impact is active, and it cuts both ways. I think the important thing about this point was that impact can be positive or negative, and a lot of associations aren't accounting for the downside risk. If your learning programs are weak, if credentials can be gamed, if there's no way to verify who actually did the work, you're not just failing to be relevant. You're actively creating negative impact and negative relevance in your market. The flip side is just as true. When an association has a learning program that's genuinely strong, genuinely verified, and backed by a track record of real outcomes, that reputation compounds. It becomes a reason members join, a reason employers recognize the credential, and a reason the association keeps mattering long after "staying relevant" would have run its course.
That distinction reframed a lot of what I heard for the rest of the conference. Every session about member engagement, every booth conversation about growth, all of it came back to whether the learning experience behind the association's brand could hold up to scrutiny.
I want to name something that came through clearly in every room I sat in: the people running these associations are not thinking about learning as an abstract strategy exercise. They're thinking about their members as real people trying to advance their careers, keep their licenses current, and get genuine value out of their membership dollars. That care is what's driving the push toward more formal, more rigorous learning programs in the first place. Leaders don't want to hand their members a credential that doesn't mean anything. They want to hand them something that actually opens doors and helps them create career impact.
The tension nobody can avoid: every association I talked to wants to build stronger, more credible learning programs, and almost none of them have the internal edtech capacity to do it at scale by themselves. That's where the partnership conversations came in, again and again. Associations know they need help from learning platforms, assessment tools, and credentialing technology to reach more members without diluting quality.
But moving all of this online, at scale, has created new problems that didn't exist when these programs meant a room full of people and a sign-in sheet. Fake learners. Shared logins. Credentials issued to someone who never actually did the work. Once a program moves online, the question stops being "is our content good" and becomes "can we actually prove who earned this." That's a hard problem, and it's one that's only getting more visible as more learning moves off the conference room floor and onto a screen.
Walking away from Indianapolis, the thread connecting all of this was pretty clear to me, and it kept circling back to that "Driven by Purpose" theme. Purpose isn't a slogan on a conference banner. It's the reason associations are building real, structured, IACET-aligned learning programs in the first place. They care about their members and they know relevance alone isn't enough anymore. But that same shift toward formal, high-stakes learning is exactly what makes verification and integrity non-negotiable. A credential is only as good as the association's ability to stand behind it, and that means knowing, with confidence, that the person on the other side of the screen is who they say they are and did the work they're claiming credit for.
That's the piece we spend our time on at Integrity Advocate, and it's why conversations like this one always feel personal to me. If your association is investing in building the kind of learning program Bill Sheehan was describing, one that creates real impact instead of just chasing relevance, let's talk about how to protect it. Book a demo with our team and we'll walk you through how we help associations secure their learning programs, verify real learners, and make sure every credential you issue actually means something.
{{post-cta}}
September 3, 2026
|
5 min de lecture
Most proctoring platforms stop at the flag. Integrity Advocate does not. This post walks through what a trained reviewer actually looks at, how a decision gets documented, and what happens if a test taker disputes the outcome, so admins know exactly what stands behind every result.
An automated flag is not a decision. It is a signal that something in a session looked different from expected, a glance away from the screen, a second voice in the room, a browser tab that opened at the wrong moment. What happens next is where most platforms stop talking, and it is exactly where the real work of assessment security begins.
For programs issuing results that carry weight, whether that is a certification, a compliance sign-off, or an academic grade, the review process behind a flag matters as much as the flag itself. Here is what actually happens.
Flags come from a mix of signals collected during the session: unusual movement, a change in lighting or audio, a browser event, an identity mismatch at check-in. None of these signals mean a test taker did anything wrong. They mean the system noticed something worth a second look.
This is the point where the two approaches to online proctoring diverge. A platform built on automated decisioning treats the flag as close to final, sometimes reducing a result to a risk score with little context behind it. A platform built on human review treats the flag as the start of a process, not the end of one.
Once a session is flagged, a trained reviewer opens the recording alongside the full context of the exam: the timestamp of the flag, the identity verification completed before the session started, and the behavior immediately before and after the triggering moment.
The reviewer is looking for the difference between a pattern that constitutes a violation and a pattern that does not, something an algorithm has no way to judge. A test taker glancing off screen to think through a problem looks identical to a system as a test taker glancing at a second monitor. A person can tell the difference in seconds. That distinction is the entire value of putting a trained reviewer behind every flag before any outcome is issued, not just the flags a system considers high risk.
{{post-stat-highlight}}
Every reviewed session results in a written outcome, not a number. That record includes what was flagged, what the reviewer observed, and the reasoning behind the final determination. This is the piece that turns a proctoring tool into a source of evidence a program can actually stand behind.
When a result gets challenged later, whether by a student, a candidate, an employer, or a regulator, the program needs more than a score. It needs a record that shows a real person looked at the specific moment in question and reached a specific, explainable conclusion. That record is what makes a result defensible.
A documented review gives programs somewhere to start when a result is questioned. Instead of pointing to an automated flag and hoping it holds up, an administrator can point to a reviewed session, a timestamped recording, and a reasoned explanation. That is the difference between a decision a program can explain and one it can only report.
This matters most in the moments programs plan for least: an appeal from a student, a compliance audit from a regulator, or a challenge to a certification result years after the exam took place. A defensible process is only defensible if it holds up when someone actually asks.
Fully automated systems are fast and they scale easily, but a score with no context is difficult to defend and carries real fairness risk. In-person testing centers solve the trust problem with human judgment, but they cannot scale and the cost is often prohibitive for programs running at volume.
Human review built into every session, not offered as a premium add-on, is what lets a program scale online without losing the judgment that makes a result defensible. As AI-assisted answer generation makes behavioral flags harder to interpret on their own, that judgment is not a nice-to-have. It is the piece of the process that automated systems cannot replicate.
Fair, trustworthy, and defensible is not a tagline. It is what a documented, human-reviewed process actually produces, session by session, for every program that runs on it.
{{post-cta}}
August 18, 2026
|
5 min de lecture
When a candidate challenges an exam result, an automated flag isn't enough to defend it. This post breaks down what "defensible" actually requires: verified identity, a documented human judgment behind every flagged session, and an audit trail that connects evidence to outcome. It also covers what regulators and accrediting bodies look for, and why liability for a flawed process typically lands on the program running the assessment, not the software vendor.
A candidate fails a high-stakes exam, and they are not willing to accept it quietly. They file a complaint. They ask their lawyer to write a letter. They ask your program to explain, in writing, exactly what happened during their exam and why the result stands.
This is the moment every compliance officer and certification director plans for but hopes never arrives. And it is the moment that reveals whether your proctoring process was ever built to survive scrutiny in the first place.
A defensible result is one your program can support with a documented, reasoned explanation, not just a data point. It means you can show who took the exam, what happened during it, how any concern was evaluated, and how the final decision was reached. If any part of that chain is missing, the result is a claim, not a record.
Most online proctoring tools were not built with this standard in mind. They were built to flag. Flagging is useful, but it is only the first step. A confidence score or an automated alert tells you that something looked unusual. It does not tell you whether that pattern was a violation, an environmental glitch, or a candidate adjusting their webcam. That distinction is exactly what a regulator, an accreditor, or opposing counsel will ask about, and "the system flagged it" is not an answer that holds up.
An algorithm can tell you that a candidate looked away from the screen twelve times. It cannot tell you whether they were checking notes, reading a printed formula sheet they were permitted to use, or glancing at a second monitor they forgot to disclose. It also cannot tell you whether an answer was written by a strong candidate under pressure or generated by an AI tool with no visible behavioral signal at all. That kind of judgment requires context, and context requires a person.
This is the gap that puts AI-only proctoring programs at risk. As AI-assisted cheating grows more sophisticated, the tools most exposed are the ones relying entirely on automated detection, because there is no human judgment behind the flag to explain what it actually means. Growing AI adoption is not a side issue for defensibility. It is becoming the central one.
Integrity Advocate is built around a simple principle: AI identifies the flags, and a trained person makes the decision. That review is standard at every price point, not something reserved for a higher tier, and it runs across the full lifecycle of the exam rather than a single monitoring window.
Before the exam. Identity verification confirms who is actually sitting the assessment, creating the first link in the chain of evidence a challenged result depends on.
During the exam. Sessions are monitored without downloads or extensions, so candidates move through the process with minimal friction while the system captures what actually occurred.
When something is flagged. A trained reviewer examines the session, applies context an algorithm cannot, and confirms or dismisses the concern based on what actually happened, not just what the system detected.
After the exam. The outcome is documented in a report that includes the verified incident, the reviewer's notes, and the supporting evidence behind the finding.
That connected process, from verified identity through to a validated result, is what separates a system that produces a defensible record from one that produces a queue of unreviewed alerts.
Regulatory scrutiny of online proctoring has increased steadily, and the pattern across jurisdictions is consistent: the organization running the assessment, not the software vendor, carries the liability. Under GDPR, the organization is treated as the data owner while the proctoring tool is the data processor, meaning responsibility for lawful, proportionate data collection sits with the program itself. Frameworks like FERPA and PIPEDA carry similar expectations for education and Canadian programs. In the United States, biometric privacy laws in states like Illinois have resulted in significant penalties tied to consent and retention practices, again with liability landing on the organization collecting the data.
Accrediting and awarding bodies apply a related lens, even when their guidance is not framed as legislation. Their central questions tend to be the same ones a court would ask: Was the assessment delivered fairly and consistently for every candidate? Was oversight proportionate, or invasive in a way that damages trust in the outcome? And if a result is challenged, is there a documented basis for the decision, or only a system-generated alert?
Programs that treat privacy as an architectural decision rather than a policy statement, meaning the system only collects what it actually needs, are in a stronger position on all three questions. So are programs that can point to a named person who reviewed the evidence, not just a threshold that was crossed.
When a result is challenged, the audit trail is the record your program stands behind. A defensible one keeps three things distinct: the signal an algorithm detected, the finding a reviewer confirmed, and the decision your program issued based on that finding. Collapsing those into a single automated step is exactly what makes a result hard to defend later.
A complete trail includes verified identity at the start of the session, the recorded evidence tied to any flagged moment, the reviewer's documented judgment on that evidence, and the final outcome connected clearly back to all of it. That structure is what allows a compliance team to answer a regulator's question in minutes rather than reconstructing the story after the fact, and it is what turns a disputed result into one your program can confidently stand behind.
{{post-cta}}
February 25, 2026
|
5 min de lecture
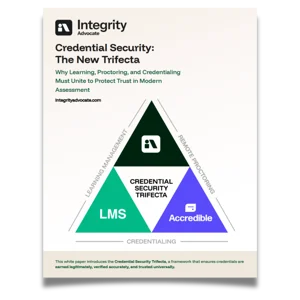
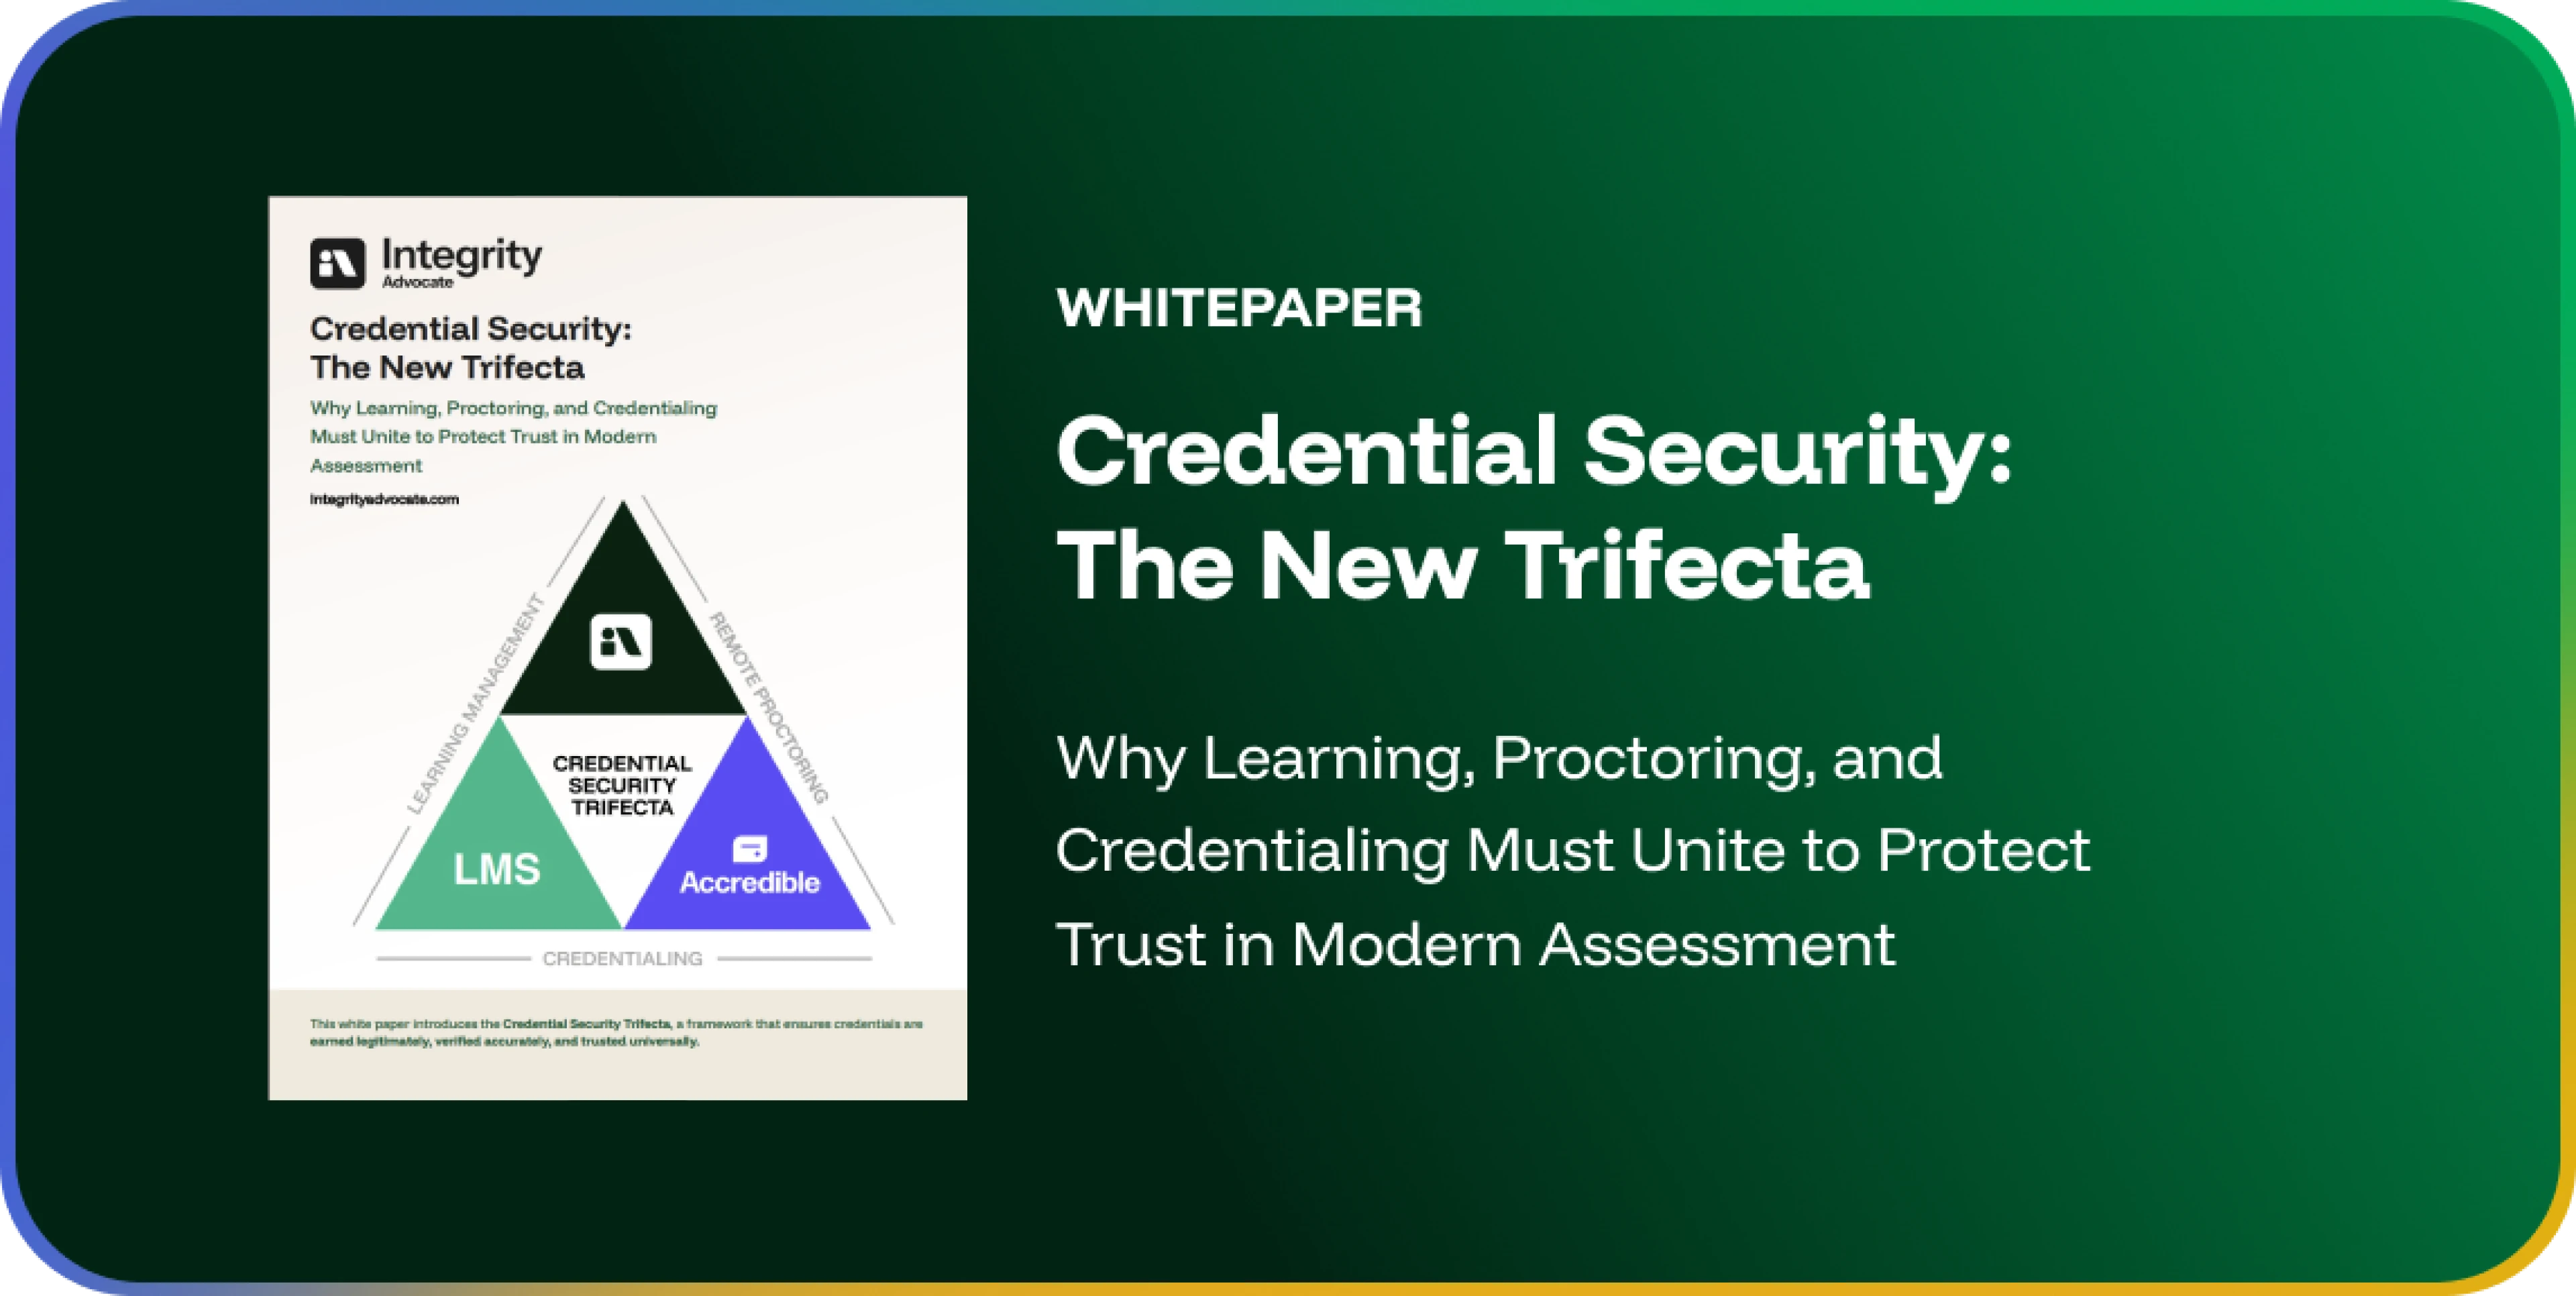
Credential integrity depends on more than a single tool. It requires identity verification, assessment oversight, credential issuance, and long-term validation to operate as one connected system. As digital credentials become more visible and portable across LinkedIn profiles and employer systems, organizations need to be able to answer a harder question than "was this test monitored": is this credential defensible? This post introduces the Credential Security Trifecta, a framework connecting Learning & Assessment Infrastructure, Identity & Integrity Verification, and Secure Digital Credential Issuance into a unified chain of trust, and points to the full whitepaper for the risk landscape, common blind spots, and an implementation model.
Credential integrity is the confidence that a credential truly represents what was earned. It means the right person completed the work, the assessment was conducted fairly, and the credential was issued based on verified performance. That confidence is built across identity verification, assessment oversight, credential issuance, and long-term validation.
As digital credentials become more visible, portable, and high-stakes, organizations are being asked a more important question: Can you defend how this credential was earned?
That question requires more than a proctoring solution. It requires a system.
In our latest whitepaper, The Credential Security Trifecta, we outline a practical framework for designing a defensible credential ecosystem, one that connects learning, verification, and issuance into a coherent chain of trust.
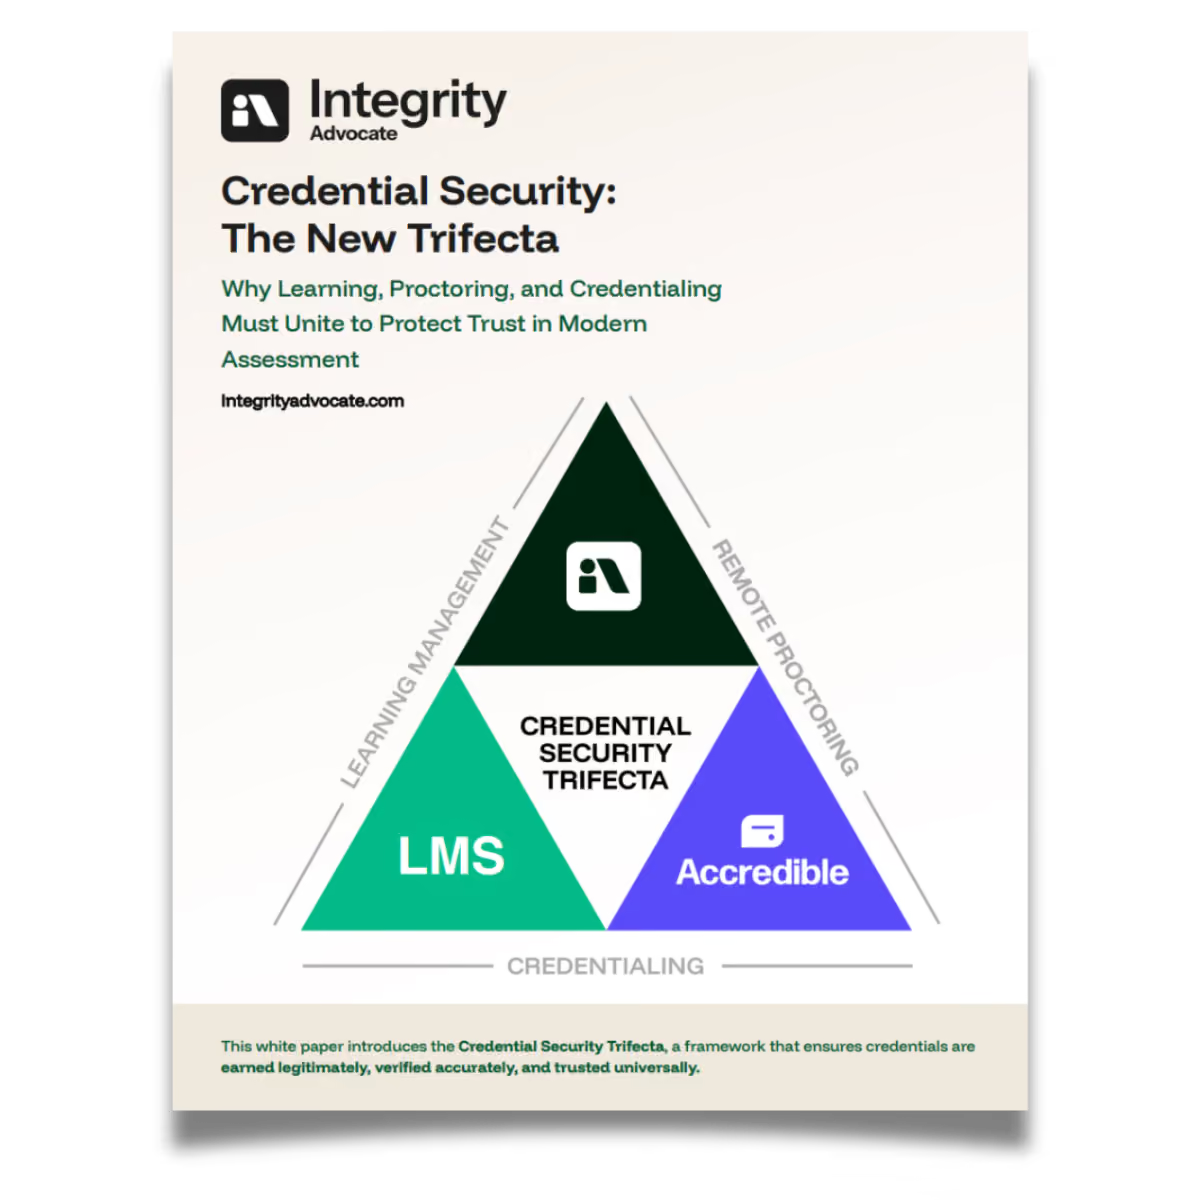
Why Learning, Proctoring, and Credentialing Must Unite to Protect Trust in Modern Assessment
For years, assessment security focused primarily on preventing misconduct during testing. That remains important. But today’s risk environment has expanded.
AI-enabled misconduct, identity fraud, contract cheating, and synthetic digital documents have changed the landscape. At the same time, digital credentials are widely shared across LinkedIn profiles, employer systems, and workforce platforms. They are public representations of institutional trust.
And the stakes are higher than ever. In an AI-accelerated world, institutions must be able to answer a fundamental question: can we confidently verify who earned this credential — and whether it was earned fairly? When credentials influence hiring decisions, promotions, licensure, and professional standing, the consequences of getting it wrong are significant.
That means the integrity conversation must move beyond: “Was this test monitored?” to: “Is this credential defensible?”
Credential security is not just about detecting misconduct. It’s about ensuring that identity, performance, and issuance are connected in a way that can withstand scrutiny.
Most organizations operate across three separate layers:
Each layer may function well independently. The risk emerges in the gaps between them. If these systems are not intentionally aligned, you may lack:
That fragmentation makes defensibility harder when questions arise from employers, regulators, or internal leadership.
The whitepaper introduces the Credential Security Trifecta, a framework that connects three essential components into a unified architecture:
Learning & Assessment Infrastructure: Where learning is delivered and performance is measured.
Identity & Integrity Verification: Where identity is confirmed, assessment conduct is reviewed, and integrity decisions are documented to ensure performance is legitimate and defensible.
Secure Digital Credential Issuance: Where verified performance becomes a tamper-resistant, independently verifiable credential.
When these three components operate as an integrated system rather than isolated tools, they form a defensible chain of trust.
This shifts the posture from reactive security to intentional design.
A defensible ecosystem does not rely on assumptions. It provides clarity. It enables leadership teams to answer, with confidence:
These are governance questions as much as technical ones. They impact compliance, employer trust, learner confidence, and institutional reputation.
Designing for defensibility requires alignment across technology, process, and policy.
The full whitepaper expands on:
It is written for certification bodies, higher education leaders, workforce programs, and assessment teams responsible for protecting credential value.
If you are evaluating how your organization connects assessment integrity with credential issuance, this framework will provide clarity.